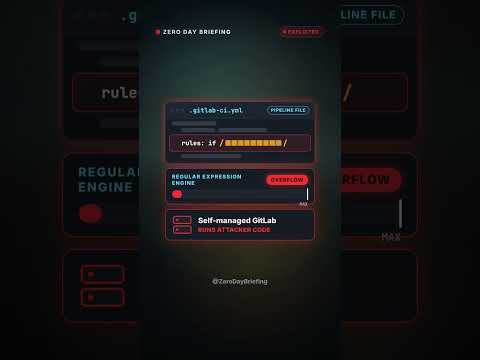
A CVSS 10.0 GitLab bug is now exploited in real attacks, and the Oct 12 fix alone doesn't fully cover self-managed GitLab.
What happened:
On Oct 29, CISA added CVE-2026-97229 to its Known Exploited Vulnerabilities list. It's an unauthenticated remote code execution flaw in self-managed GitLab CE/EE, triggered by a crafted regular expression in a CI/CD configuration.
Why the Oct 12 patch isn't enough:
A sibling bug in the same regex compiler, CVE-2026-110264 (also CVSS 10.0), was patched on Oct 21. That means 19.4.2, 19.3.5 and 19.2.8 are still vulnerable to it.
What to do:
Update to 19.5.1, 19.4.3, 19.3.6 or 19.2.9 (or newer). The only fix is to upgrade. GitLab.com and GitLab Dedicated are already patched.