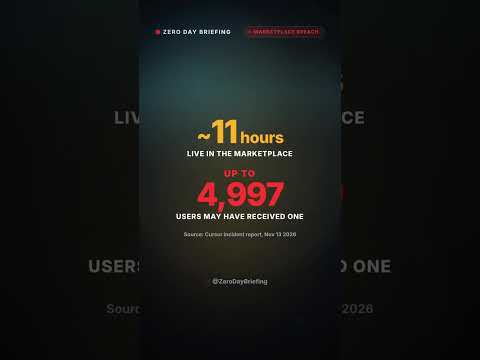
Use Cursor? Check your Claude Code extension version now. Per Cursor, fake copies were served from its marketplace for about 11 hours.
What Cursor says happened:
- On Oct 29, an attacker used a stolen credential to place unauthorized copies of Anthropic.claude-code 2.1.312 and 2.1.313 (Windows and macOS) on the cache serving its marketplace.
- Up to 5,000 users may have received one.
- The fake tried to add an attacker SSH key labeled svc-telemetry to ~/.ssh/authorized_keys for later access.
- Anthropic did not publish these copies, this is not a vulnerability in Anthropic's product, and Open VSX never had the malware.
What to check:
- Is your Claude Code extension version 2.1.312 or 2.1.313?
- Look in authorized_keys for a key labeled svc-telemetry.
- Uninstalling alone may not be enough, because persistence scripts can keep running. Use Cursor's check and remediation scripts, remove the key and persistence, and rotate credentials reachable from that machine.
Sources:
https://cursor.com/blog/security-incident-update
https://cursor.com/blog/claude-code-extension-security-notice