An 11 year old critical NGINX flaw (CVE-2026-123007, CVSS 9.2) is finally fixed.
Only servers with HTTP/2 enabled are affected.
The vendor lists no workaround.
Fixed in NGINX 1.31.9 (mainline) and 1.30.7 (stable).
No attacks reported so far.
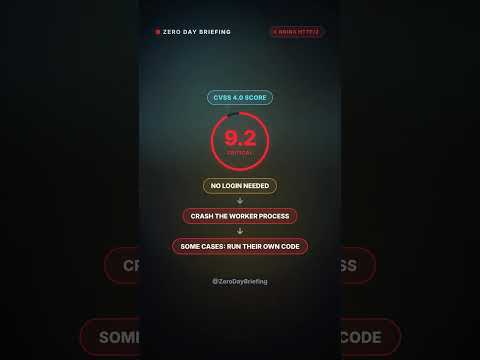 Play the video: NGINX 11 Year Old Critical Flaw Fixed: Are You Exposed?
An 11 year old critical NGINX flaw (CVE-2026-123007, CVSS 9.2) is finally fixed.
Only servers with HTTP/2 enabled are affected.
The vendor lists no workaround.
Fixed in NGINX 1.31.9 (mainline) and 1.30.7 (stable).
No attacks reported so far.