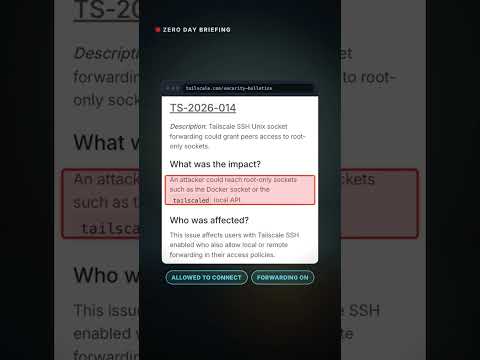
A normal user can become root through Tailscale SSH. Researchers call the bugs "Tailworm".
Cyberdione Labs published its findings before a patch was released. The worst one hits Tailscale SSH.
A user who is already authorized to connect, with forwarding allowed in the access policy, could reach root-only sockets like the Docker socket or the tailscaled local API. The researcher demonstrated root access in a lab.
This is privilege escalation by an authorized user. It is not a remote attack without login. No exploitation has been reported.
FIX: Update to Tailscale 1.104.4 or newer (security bulletins TS-2026-014 to TS-2026-017). Update servers first.
CAN'T UPDATE YET: Set TS_SSH_DISABLE_FORWARDING=1 in the tailscaled service environment and restart it. Also limit who can use Tailscale SSH in your access policies.
Sources: tailscale.com/security-bulletins, BleepingComputer (Oct 27 2026)