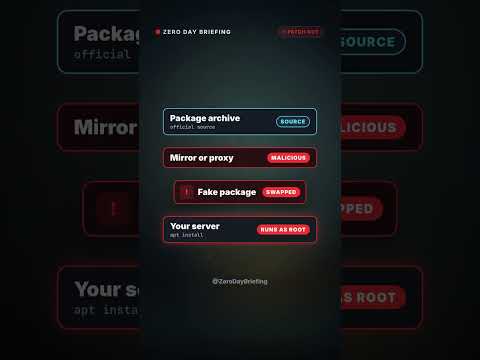
A fake package can install with root control on Ubuntu and Debian (CVE-2026-109518). Patch now.
The APT flaw lets an attacker who can tamper with your download traffic swap in an unverified package.
Who is affected:
Debian 12, and Ubuntu 22.04 and newer, are exposed by default because Acquire::Retries defaults to 3. The attacker needs a position on your download path, such as a malicious mirror or proxy.
Severity:
CVSS 4.0 score 7.7 (High), rated by Canonical.
Status:
Fixed on 4 Nov 2026 (DSA-6607-1, USN-8996-1). There is no known exploitation. Ubuntu 20.04 and older get the fix through Ubuntu Pro (ESM).
Fix:
sudo apt update && sudo apt upgrade
Also: only use mirrors you trust.